

 LinkedIn
 Xing
 Email

Identify IT risks. Strengthen compliance. Ensure resilience.
Today, digital technologies form the foundation of almost every business process. At the same time, the demand for information security, data protection, compliance and effective IT risk management is growing. Cyberattacks, regulatory requirements and the increasing interconnectivity of systems are making the IT landscape more complex and presenting companies with new challenges.
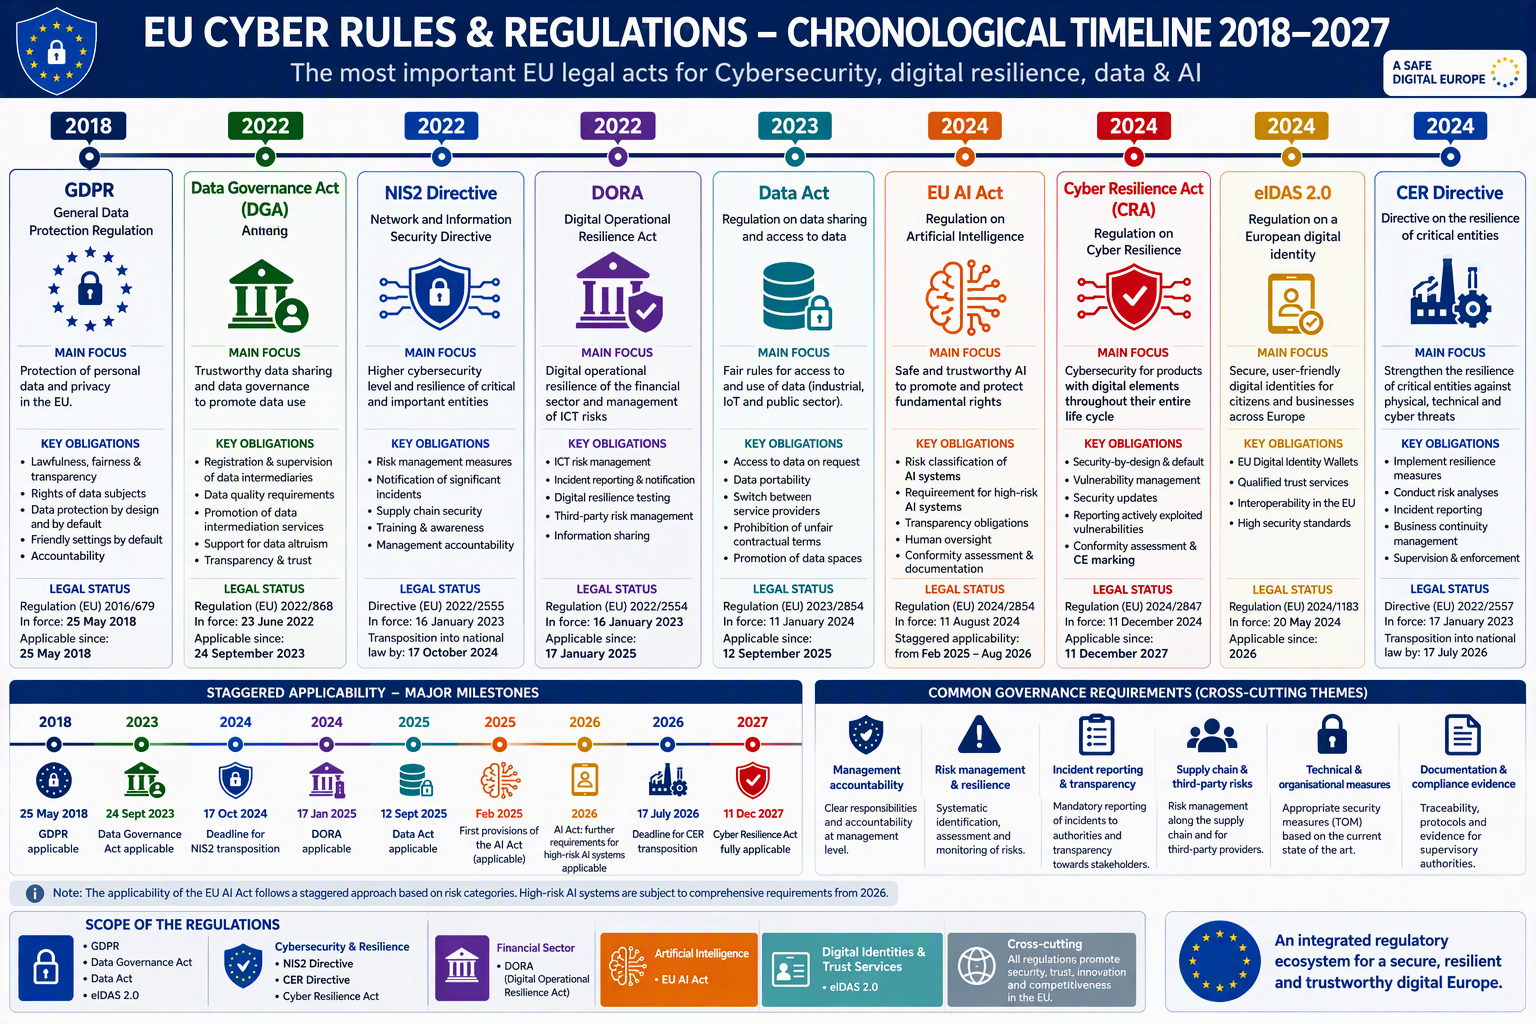
The European Union has responded with a comprehensive regulatory framework. Regulations such as the NIS2 Directive, the Cyber Resilience Act (CRA), DORA, the AI Act, the Data Act and other guidelines are introducing new requirements in the areas of governance, risk management, reporting obligations, supply chain security and technical safeguards. Companies must not only comply with individual regulations, but also take a holistic view of the regulatory requirements and integrate them into their security and compliance strategy.
Those who address regulatory obligations at an early stage and systematically manage cyber risks not only strengthen their own compliance, but also enhance digital resilience, protect business-critical processes and build trust among customers, business partners and regulatory authorities.
The overview sets out the key European legislative acts and their chronological order in the areas of cybersecurity, digital resilience, data regulation and artificial intelligence.
IT Audit and Cyber Advisory from a Single Source
In today's world, secure and reliable IT is a critical success factor. We audit your IT systems, processes and internal control mechanisms, analyse risks and evaluate the effectiveness of your existing security measures.
Through risk-based audits, data analysis and independent assessments, we provide transparency regarding your IT organisation's maturity level. This allows you to identify vulnerabilities, mitigate risks and make informed decisions regarding the future development of your IT infrastructure.
NIS2 Compliance and Cyber Resilience
The NIS2 Directive introduces tighter requirements for cybersecurity, risk management and governance. Many companies are facing the challenge of implementing these requirements while also trying to increase their resilience against cyberattacks.
We can guide your company towards NIS2 compliance, assisting with impact assessments, gap analyses and the implementation of organisational and technical security measures. This lays the groundwork for greater cyber resilience, sustainable information security, and the secure fulfilment of regulatory requirements.
IT Audits as the Foundation for Informed Decisions
Efficient business processes and sustainable corporate success depend on high-performance, secure and compliant IT. Our IT audit services help you to assess the effectiveness, security and compliance of your IT processes, systems and controls. We analyse IT risks, identify opportunities for optimisation and provide transparency regarding the maturity level of your IT organisation. This provides management, the internal audit team, supervisory bodies and auditors with a solid basis on which to make decisions that will strengthen IT governance, information security and compliance in the long term.
Cyber Risks Throughout the Entire Enterprise Lifecycle
Cyber risks can arise in a variety of business contexts. This is why we provide targeted support in areas where transparency and security are of particular importance.
Preventive Cybersecurity & IT Compliance
Effective protection against cyberattacks requires more than just individual security measures. Companies must systematically integrate recognised information security standards and regulatory requirements into their processes, continuously refining them as they do so.
We can help you analyse, select and implement relevant compliance and cybersecurity requirements, and guide you through the implementation of industry-specific security requirements and regulatory guidelines. These include NIS2, ISO/IEC 27001, DIN SPEC 27076, the EU AI Regulation, KRITIS requirements, the BSI Basic Protection Framework and the Cyber Resilience Act (CRA), among others. We also conduct a cybersecurity check (health check) based on Locate Risk.
Our focus is on practical and cost-effective implementation within existing IT and business processes. We support you in sustainably strengthening your IT security, compliance, and cyber resilience, and in meeting audit requirements in a transparent manner, from gap analysis to the implementation of appropriate measures and audit preparation.
Reactive Cybersecurity, Incident Response, and Crisis Management
A cyberattack or security incident requires swift and coordinated action. We support your company’s crisis management efforts, containing cyber incidents effectively, minimising damage and stabilising business operations as quickly as possible.
As part of our incident response services, we coordinate the necessary measures and facilitate communication with government agencies, cyber insurance providers, affected business partners and external service providers. At the same time, we assist with securing affected systems, IT, forensic analysis, documenting the incident and implementing appropriate immediate and protective measures to restore IT security.
We also facilitate collaboration with data protection supervisory authorities and law enforcement agencies, as well as damage assessment and post-incident follow-up. This helps you to minimise the impact of a cyberattack, meet regulatory requirements and strengthen your company’s cyber resilience in the long term.
Why Nexia?
Our cyber advisory, cybersecurity, information security and IT risk management experts have many years of experience across various industries, roles and project scenarios. This diversity enables us to take a holistic view of technical, organisational and regulatory requirements, developing practical solutions in the process.
As trusted advisors, we support our clients throughout the entire process, from initial analysis and workshops to design and implementation, ensuring the sustainable integration of new processes. In doing so, we facilitate targeted knowledge transfer, coordinate various project stakeholders as required, and ensure transparency regarding progress, risks, and necessary actions.
By providing a single point of contact and structured project management, we reduce the coordination burden on our clients and ensure that their transformation, cybersecurity, and compliance projects are implemented efficiently and purposefully.
Identifying cyber risks. Targeted mitigation of security vulnerabilities.
Companies are increasingly becoming the target of cyberattacks. Our vulnerability analysis reveals which of your information, systems and potential security gaps are visible on the internet. We assess technical and organisational risks, identify vulnerabilities and establish a robust basis for measures aimed at strengthening your cyber resilience, IT security and compliance.
Contact persons
Do you have any questions or do you need support?
Please contact our specialists.
You will find a complete overview of our contact persons on our team page.